Search results for RedTeam
RedTeam community
One keyword maps to one global community path.
People
Not Found
Tweets including RedTeam

True identity behind every alias.
RedTeam/Innerworks anchors identity to the device, past every fresh wallet, account, or browser they spin up.
Live across every client: fraud, multi-account abuse, and tracking sanctioned actors across burner identities.
Observed on a single client platform: 1 in 5 requests originated from a single device. A pattern that recurs across deployments at varying severity
Shipping out of Subnet 61.
Show more


ChatGPT agrees with you too much.
Type these before your prompt:
TRUTHMODE: brutally honest
REDTEAM: plays devil's advocate
SOCRATES: teaches through questions
LINDYMODE: uses proven methods, not hype
10 codes + hundreds more:
Show more


This past week in Bittensor Land:
- @oroagents was accepted into Y Combinator’s Fall 2026 batch, making it the first crypto company with a live token to be accepted into YC.
- @lium_io conducted a $1M revenue-funded buyback and burn, the largest single buyback in Bittensor history.
- @_redteam_ announced that it is on track for integrations with three banking companies in the top 10% of the Fortune 500.
- @conjectures_io reported that miners found a solution to the near-half-density case of Green’s Problem 51, a math problem that had remained open for 16 years.
- @jon_durbin of @chutes_ai shared a dashboard for the Parallax-8B training run, an MoE model being training on 240 RTX 5090s distributed across 13 countries, with a reported compute cost of only ~$11/ billion tokens (!).
Just another week.
Show more
Every month for eleven months, we tested every major bot detection vendor against a continuously growing set of real attacks and measured each one's true detection rate. The attacks came from two sources, miners who competed in RedTeam's humanize_behaviour challenges to generate human-like bot behaviour, and attacks built in-house by our team.
Over this period, the average detection rate among these vendors decayed from 59% to 14.6%. Even the market leaders dropped by over 50%.
Meanwhile, our detection rate jumped from 74.3% to 99.5%.
The attacks these vendors failed against in testing are the same ones we find sitting in live traffic when clients switch to us from these providers. Our miners aggregate methods used by the most dangerous fraud operations on the internet and continuously sharpen them with techniques of their own. The reason we can compound against these frontier attacks while other vendors degrade is that every attack is instantly reverse-engineered and folded back into the system.
Next month, we release the immune system alongside our new bot virus challenge. It's exactly what the name suggests, an evolving system that keeps improving while the market around it degrades, and one built to generate and neutralise attacks that don't yet exist anywhere in the wild. We believe that as AI continues to advance, this is the only defense structure that survives.
Stay tuned.
Show more


🛡 TL;DR: an open-source red teaming framework that calls itself "penetration testing, but for LLMs."
Title: confident-ai/deepteam
URL:
📌 Highlights
🎯 50+ vulnerabilities across 6 categories: data privacy, bias, authorization bypass, agent-specific risks and more
⚔️ 20+ attack methods, from prompt injection to multi-turn crescendo jailbreaks
📋 Aligned with OWASP Top 10 for LLMs/Agents, NIST AI RMF, MITRE ATLAS and other industry standards
🔒 Evaluation runs entirely locally, no data sent externally
🚦 Ships 7 real-time guardrails like ToxicityGuard for production use
⭐ 2.8k GitHub stars, 1,187+ commits and active ongoing development
Just `pip install` it and pass your model callback, that low barrier to entry makes it easy to actually adopt.
#LLMSecurity# #RedTeaming#
Show more


@RedTemplars23 🖤🐦⬛


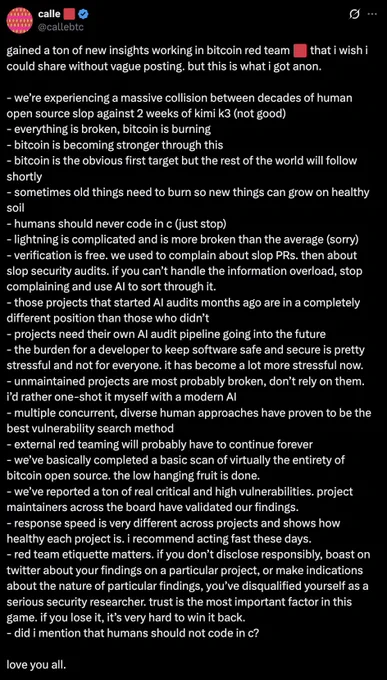
'Bitcoin Is Burning': Red Team Turns to Chinese AI to Find Flaws

Kimi K3 Scan Uncovers Critical Vulnerabilities Across Bitcoin Open-Source Projects
Bitcoin Red Team researcher calle said that after using Kimi K3 for two weeks, the team identified numerous critical and high-severity vulnerabilities across Bitcoin open-source projects, with maintainers validating the findings. The team has completed a basic scan of nearly the entire Bitcoin open-source ecosystem, with many of the easier-to-find vulnerabilities already discovered.
Calle said AI is significantly lowering the cost of vulnerability discovery and verification, making unmaintained projects increasingly risky. He argued that projects will need to establish their own AI-driven security audit pipelines, while the speed of response to vulnerability reports has become an important indicator of project health.
Show more

AI-Infra-Guard is an open-source, self-hosted red-teaming platform for AI builders.
• Scan AI infrastructure for fingerprints and CVEs
• Audit MCP servers and Agent Skills
• Red-team Agent workflows and LLMs
• Run locally with Docker; integrate via Web UI or API
Build with more visibility:
Show more
