
Charles Guillemet
@P3b7_
CTO at @ledger. Busy securing the blockchain revolution. Cryptography, (Hw) Security, Tech, Blockchain.
Previously built the Donjon (@DonjonLedger)
310 Following 46.3K Followers
You thought this was a bad week in crypto? You might have missed the bigger news.
Two results just landed on elliptic-curve cryptography. Both are worrying. Neither one breaks a key anyone uses today.
1️⃣ The problem under ECC is less hard than we thought.
ECC is secure because the elliptic-curve discrete log is hard. The best general algorithm we had was Pollard's rho, and it is exponential: add bits to the key, and breaking it gets exponentially harder.
That assumption is now false, with one caveat. A paper from Bochum and MPI-SP gives a subexponential algorithm. It assumes an OpenAI claim that is still under review. If the claim holds, the new algorithm is faster asymptotically. In practice it changes nothing. On secp256k1, P-256, or Ed25519, rho is still the best algorithm, and it still takes the age of the universe. The new one only pulls ahead on hypothetical curves of enormous size, and there the cost is even more absurd.
2️⃣ The quantum circuit is getting cheaper. The computer is not here.
We still have no quantum computer. The circuit that would run on one to break ECDSA keeps getting cheaper. is a public auto-research loop aimed at exactly that. Its current best is about 70% cheaper than the circuit Google reported, on logical qubits times Toffolis (0.91 billion against 2.99 billion). Google's circuit was already two to three times cheaper than the previous published one.
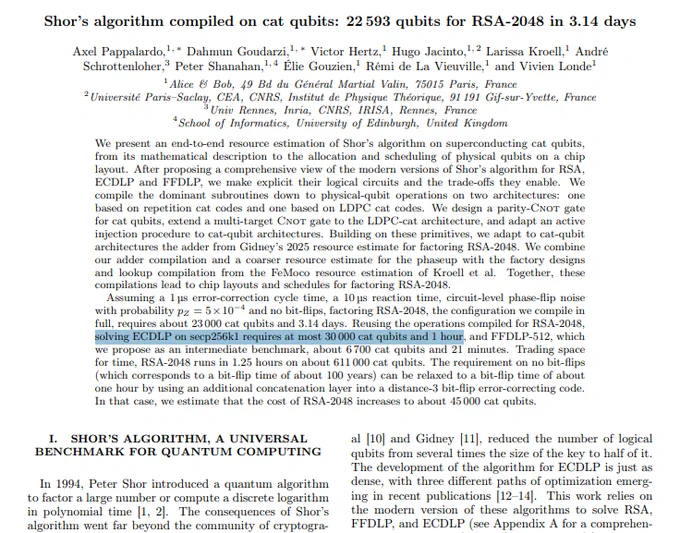
Alice & Bob @Alice__Bob , a French Quantum Computing company, just estimated that breaking secp256k1, the Bitcoin curve, takes at most about 30,000 cat qubits and one hour. That figure assumes a machine nobody has built. We are still far from it. The machine being asked for keeps getting smaller.
What a crazy time to be alive.
Show more


It's time to use one of these vulns to reset the simulation 🫠

🤖ETH (not Ethereum but the Exponential Time Hypothesis) is false.
A Lean proof, produced by OpenAI says 3-SAT can be solved in subexponential time.
For twenty-five years the field assumed the opposite, and hundreds of "impossible unless ETH fails" results in graphs, biology, databases, and geometry were deduced from a false premise.
The problems are not suddenly easy. We have simply lost a fundamental reason we had for refusing to look for a faster algorithm. Sorry, your SAT solver does not get faster.
ETH was the strong form of P ≠ NP. Every polynomial is already subexponential, so a true ETH would have implied P ≠ NP immediately. A false ETH does not imply P = NP. Subexponential is still FAR more than polynomial.
This has no impact on cryptography. Signatures, hashes, discrete logs, and lattices are average-case questions about specific functions. A faster worst-case algorithm for Boolean formulas does not forge a signature, invert SHA-256, or change the cost of a Bitcoin block.
Classical cryptography needs one-way functions, and those cannot exist if P = NP.
Whenever P = NP is proven, our simulation must be reset.
Show more
Could be a good idea to disclose this to Microsoft first...

Just found a zero day
If you right click on an executable on Windows, select run as administrator, it will run as administrator
I'm calling it Program2Shell
Security is already incredibly difficult, and now we have researchers doing full disclosures... 🫠

‼️ Researcher Erica Windisch skipped coordinated vulnerability disclosure and published 11 unpatched Tailscale flaws.
In her lab, Tailscale SSH race conditions let one hacked device get root on other servers and add a rogue node.
Show more


Bitcoin is often compared to gold. But Bitcoin is superior.
- It’s easily transferable across the planet in minutes.
- It’s divisible down to 100 million sats: no melting, no weighing.
- Self-custody means no vault fees or seizure risk beyond losing your keys.
- And contrary to gold, there’s a hard finite amount of Bitcoin: 21 million. Gold’s supply can keep growing via mining or, as Marathon Fusion is demonstrating, via nuclear transmutation of mercury using fusion neutrons. Physical scarcity might be a temporary geological constraint. Bitcoin’s is mathematical and fixed by protocol.
Show more

Last month, we demonstrated high-rate alchemy: turning mercury into real, stable gold, beating CERN’s record by a factor of 10.
Last week, we enriched isotopes in the world’s most powerful plasma centrifuge, beating the Soviet record that stood for 40 years.
Now, we’re building a fusion reactor in San Francisco to achieve record power density.
Show more

🧵Yesterday may prove to be a turning point for security.
AI is making vulnerability research dramatically faster. This favors attackers: they can find vulns and exploits at machine speed, while organizations must still inventory systems, test updates, and deploy patches without breaking production.
PHP2Shell shows what that looks like.
On August 11, researchers reported critical flaws in PHP runtime. They had existed for more than a decade and affects versions from PHP 5.4. An unauthenticated attacker could potentially execute code remotely, read process memory containing passwords, tokens, and API keys...🫠 Both vulnerabilities are rated CVSS 9.2.
PHP powers roughly 70% of websites, totalling millions of servers.
The researchers disclosed the bugs responsibly. Fixing them took about 70 days. The fix touchs 300+ files and changed nearly 12,000 lines. These were not simple mistakes.
The disclosure then broke down. Amazon saw an apparent exploitation attempt on October 17, four days before the public release. This indicates a first leak. On October 20, the CVE identifiers leaked. The next morning, a supplier with advance access published patched container images more than six hours early, giving attackers a chance to study the fix while most defenders were still waiting.
The official releases arrived at 14:00 UTC. Exploitation followed immediately. Cloudflare reported thousands of attempts in the ten hours before the announcement, tens of thousands in the first 45 minutes, hundreds of thousands within two hours, and millions later that day.
Organizations that could not patch immediately had incomplete options: WAF rules, isolation, or taking services offline. Government portals, universities, and hospitals across Europe did exactly that.
Large teams with accurate inventories and automated deployment could respond in hours. Many others still do not know where PHP is running: an old site, a vendor appliance, a forgotten container, or an unsupported internal application.
AI did not make software insecure. It always was insecure. AI just changed the economics of finding and exploiting bugs and compressed the gap between disclosure and mass exploitation from days to minutes.
Patching faster will not be enough. Critical systems need continuous inventory, automatic updates, isolation, memory-safe languages where possible. Our last bastion is software whose security can be demonstrated rather than assumed: formal verification, cryptography, memory-safe architectures, and secure hardware.
The era in which complexity provided accidental protection is ending. PHP2Shell is not an isolated crisis. It is a preview.
Show more

This is the speed of vulnerability exploits now... 🫠
Some stats on #php2shell#. In the 10 hours before it was publicly announced, across the @Cloudflare network we saw thousands of attempts to exploit it. That jumped to tens of thousands in the 45 minutes post announcement, hundreds of thousands within 2 hours, and millions now.
Show more
I wonder what the game theory says about this. I guess we'll find out

JUST IN: Liquid L-BTC swaps back online at 1:1 for real Bitcoin, although reserves still short of 602 BTC.
Bit⚡️Dov @bitdov suggests the federation already has an internal agreement to cover it.
Show more


Breaking the embargo just facilitated early exploitation...

Two critical PHP vulnerabilities (CVSS 9.2) were disclosed today, allowing unauthenticated RCE on default configurations.
To help everyone patch fast we are making images for PHP 8.2, 8.3, 8.4, and 8.5 free for anyone to use. You can access them here:
Coordinated disclosure is hard, we appreciated everyone's help as we worked through this over the last several days.
Show more

You finally patched PHP, node.js and assessed your exposure to TLS?
Don't forget to have a look at Gitlab 🫠

🚨 CRITICAL: GitLab flaw (CVSS 10.0) affects 12 years of releases.
CVE-2026-110264 could allow unauthenticated remote code execution on self-managed servers.
Read -

No debate. Today was worse than the entire year. And the worst part is, days like this are about to become more frequent.

Arguably, these vulnerabilities collectively make up the single most consequential day for security on the internet, purely in terms of the numbers of users and websites affected (billions)
This one aged way too well 🫠
Imagine you wake up and:
- PHP has two critical vulnerabilities, rated 9.2, and exploitation has already started, even before the fix was published. There's not fix for old versions...
- Node.js has four high vulnerabilities, including arbitrary code execution.
- Eight TLS intermediates have private keys of 3 to 8 bits. I don't believe in conspiracy theories, but...
All of this is in the field. Millions of machines are vulnerable. Most of them will not be patched in the near future and you can't really trust TLS anymore...
The state of security is really, really frightening. And it won't get better anytime soon. 🫠
Show more

For once, vulnerabilities were found before they were exploited in the wild, giving developers a window of time to update.
As soon as it's out, exploits will follow very quickly.

‼️ PHP Warns of Two Critical 9.2 Security Vulnerabilities, Urges Users to Prepare for Patches
Details:
The PHP security team has warned users about two critical vulnerabilities and urged administrators to prepare for an upcoming security release.
Both flaws carry a CVSS v4.0 score of 9.2. Updates are scheduled for Wednesday, October 21, 2026, at 14:00 UTC, giving website owners and hosting providers a short window to prepare. Public reporting links the upcoming fixes to CVE-2026-109618 and CVE-2026-109619.
Security firm watchTowr describes them as reported remote code execution vulnerabilities, which could allow attackers to run their own code on affected servers. However, PHP’s advance notice does not name the CVEs or explain how the flaws work. Reports suggest the vulnerabilities could affect PHP versions from PHP 5 onward.
#cybersecuritynews#
Show more


PHP is shipping a security release tomorrow, Oct 21, at 10:00 AM ET for two critical vulnerabilities, rated CVSS 9.2 per @ThePHPF. It could land earlier if details go public or exploitation shows up.
@watchtowrcyber says details already leaked, that both are remote code execution, and rates them a 10. PHP hasn't confirmed any of that, but plan like it's true.
Tonight: find every place PHP runs, check versions with php -v and php-fpm -v, and line up a patch window for the morning. Anything older than 8.2 is end of life, so don't expect a fix there.
Every PHP install without an owner is attack surface you can cut today.
Show more
The NIST curve seeds were a clock. There was no hidden story. That reminded me the DES story.
Most blockchains still prove ownership with ECDSA, and will until the post-quantum migration. NIST standardized the EC curves on year 2000.
But Bitcoin uses a non-standardized curve: secp256k1. We don't know for sure why he didn't choose the standard curve. The suspicion, that the NIST seed might hide a backdoor is a commonly shared assumption.
The cost shows up in Hardware support. Apple's Secure Enclave and Android StrongBox sign NIST P-256, also called secp256r1 ("r1", not "k1"). A Bitcoin key cannot be generated there, and it cannot sign there, same for many secure hardware.
A few days ago, Anthropic published where those seeds came from: Claude reveals ECDSA curve origins. They are output from lrand48, the C library generator, started by srand48 from a Unix timestamp. For P-256 the clock is 16 August 1997, 01:52:34 UTC, and the published seed is candidate 1,842. The same generator recovers the other NIST prime curves. The reproduction is a few dozen lines.
Large enough quantum computers would break ECDSA on both curves. So we still have to migrate Bitcoin towards PQC. And in the meantime, we know that secp256r1 was not backdoored by the NIST.
It might improve our trust in the new PQC standards selected by ... the NIST!
Show more


When Cellebrite unveils a zero-day, you can be assured that everyone is already aware and that its value is zero.
It's just that it can't be patched.
‼️BREAKING: Cellebrite unveiled zero-day LOKI, a boot ROM exploit for Apple chips from iPod touch 2 to iPhone 11.
Its Hexacon slide calls it a timing race that some early proofs of concept won just 1 in 25 times.
Boot ROM code is burned into the chip. No update can fix it.
Show more


Huge presentations from the Calif team at Hexacon! Live demo of an untethered jailbreak on iPhone 18 Pro running iOS 27.0.1 that survives reboot with root access, plus Signal 1-click and iMessage attacks.
Recreating the security balance we used to have is going to be difficult
Show more

Demos we presented at Hexacon in Paris today. Everything will be released in due time.
1/ Signal 1-click

Relive the moment @_pgauthier, Chairman & CEO, revealed Ledger Atom™ at Ledger Op3n in Paris: the device built to protect everything you value.
Our first device with your everyday apps and 5G connectivity built in, switching to Secure Mode whenever you interact with your private keys.
Show more











