
23pds (山哥)
@im23pds
6K Following 15.9K Followers

One thought for wallet teams: it may be helpful to gently remind users when they open the app on an iOS version that isn’t up to date. A small reminder could help users stay a little safer.🫡
🚨 SlowMist TI Alert: DarkSword Targets iPhone Crypto Users
⚠️ iPhone and iPad users: Update your iOS promptly and beware of apps potentially compromised by #DarkSword#.
DarkSword targets crypto users, exploiting iOS vulnerabilities to escape the sandbox and steal sensitive data, including Keychain credentials, locally stored wallet private keys, and Notes data. Successful exploitation could put your crypto assets at risk.
🔎 According to SlowMist’s MistEye threat intelligence analysis, 1,500+ DarkSword-related phishing sites have been identified across the web, targeting users through e-commerce platforms, fake Binance and OKX sites, fake crypto wallets, gaming services, and cryptocurrency exchanges.
🛡️ Stay safe:
• Keep your iOS devices updated.
• Be cautious of suspicious or compromised apps.
• Never store sensitive wallet credentials or seed phrases in Notes.
📖 Related SlowMist analyses:
🔗 DarkSword Trojan Backend & iOS Attack Chain:
🔗 FomoPeek App Store Poisoning & iOS Kernel Exploitation:
Show more


Keep your iOS up-to-date.

Our security researchers built an autonomous cyber vulnerability discovery, exploitation, and patching pipeline.
In a single run with an upcoming cyber model, it validated and generated patches for 948 local privilege escalation vulnerabilities in the Linux kernel at a total API cost of $1.2 million.
Show more

🚨 SlowMist TI Alert: Beware of bookmark-based phishing attacks targeting the @fomo web interface 🚨
The phishing page tricks users into completing a fake CAPTCHA, then instructs them to drag malicious JavaScript code into the browser’s bookmarks. After just 2–3 clicks on the malicious bookmark, attackers can hijack a previously logged-in FOMO account and immediately steal its crypto assets.
This is not a new technique. It’s an old exploitation method previously.
Stay alert, and watch for our upcoming analysis.
Show more


Before sending crypto, take a few seconds to check where you are and where your funds are going. #punycode#
Stay vigilant!

🚨 UPDATE: SlowMist says malicious activity tied to Bitget’s $388M hack began Aug. 31 before draining hot wallets on Sept. 24.


Following an investigation into an infrastructure compromise, MetaMask Staking (ex Consensys Staking) has taken precautionary steps to protect client assets related to its operated Ethereum validators.
These steps include exiting its Ethereum (ETH) validators in the Lido protocol, and will likely incur foregone rewards as well as possible downtime penalties should validators be taken offline in the near future to reduce risks related to potential network penalties. Relevant validators have begun the exit process, with the final validators expected to be exited (but not fully withdrawn) by the end of October 7th, 2026.
No action is required from stETH holders. ETH exited from MetaMask Staking-operated validators is expected to return to the protocol gradually as the relevant validators complete the exit, withdrawal, and re-entry cycle, which is estimated to take approximately up to 45 days due to the extended entry queue. As a reminder, staking operations are non-custodial in nature and MetaMask does not manage withdrawal keys for staking on behalf of clients.
As always, the Lido Protocol’s diverse Node Operator set and other security systems including the ad hoc reserve fund (of over 6,750 stETH), are designed to contain and mitigate disruptions to the normal operations of the protocol, in addition to other potential routes.
A full investigation is underway, and further updates will be shared as they become available. For further details, please refer to the MetaMask Staking release linked below.
Show more


Security Update: We are responding to a security incident affecting part of our infrastructure.
At this time, we have identified no immediate threat to MetaMask wallets.
As a precaution, we are proactively exiting affected validators within our non-custodial staking operations, in coordination with clients, partners and security advisors.
We’ll share further updates as appropriate.
Show more


We are very grateful for SlowMist's quick response and professionalism in helping us investigate this incident thoroughly. They have shared their findings on the September 24 security incident.
Their investigation identified malicious activity involving third-party security products, including a zero-day vulnerability, and recovered a customized tool used by the attacker to initiate unauthorized withdrawals.
The findings align with the attack path we previously shared and add further detail on how the incident unfolded.
Our focus is firmly on what comes next: applying these findings, continuing to strengthen our security controls and continuing to protect our users and their assets.
Show more
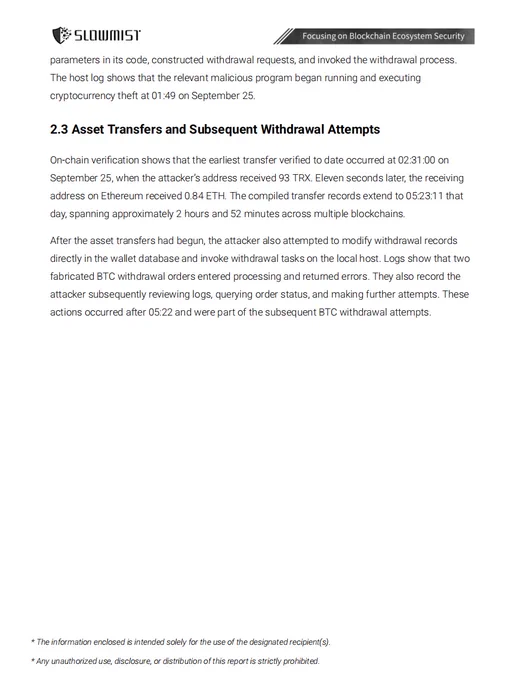
@bitget has engaged SlowMist’s security team to investigate the September 25 hot wallet asset theft.
As of September 29, our investigation has identified malicious activity involving certain third-party security products and a wallet application host, as well as a highly customized withdrawal tool used by the attacker.
🔎 Key findings include:
1. Malicious activity on a certain third-party product involving exploitation of a zero-day vulnerability.
2. Unauthorized access to a certain third-party products management platform on September 25 using an internal employee identity.
3. Recovery of a customized withdrawal tool designed to interact with the wallet system’s withdrawal logic.
4. On-chain activity begins at 02:31 on September 25, with transfers across multiple blockchains over approximately 2 hours and 52 minutes.
5. Subsequent attempts to manipulate withdrawal records and trigger additional BTC withdrawals.
We are continuing to investigate how the attacker moved between the affected systems.
All date references are to UTC+8.
📄 Read the details of the investigation:
Show more

Critical RCE Alert: Full takeover of HashiCorp Vault and OpenBao.

🚨SlowMist Alert🚨
💸 @MoonwellDeFi Loss: ~$8.7M USD
🔍 Root Cause: The protocol relied on a MAMO price from a thin market. The attacker manipulated this price, making the collateral appear far more valuable than it really was. This allowed the attacker to borrow funds from the mUSDC and mcbBTC markets and profit from the inflated collateral value.
📌 Attacker: 0x719eae70d4a83f35bf82a2740699f5db84be919d
📌 Vulnerable Contract: 0xf877acafa28c19b96727966690b2f44d35ad5976
📌 Collateral Market: 0x2f90bb22eb3979f5ffad31ea6c3f0792ca66da32
Powered by
Tx:
Show more
🚨 Job Scam Alert: Interview Software Used to Deliver Info-Stealing Malware
MistEye has identified a job scam campaign targeting Web3 professionals. Threat actors are impersonating recruiters and luring victims into installing a malicious application disguised as an AI meeting tool called “Relay”.
The malware targets both macOS and Windows users, attempting to steal sensitive data including browser credentials, wallet-related information, Keychain data, Telegram sessions, and more. We analyzed the samples and revealed how this attack chain was built.
Please remain cautious when installing software during online interviews or recruitment processes. Avoid executing unverified applications and carefully review unexpected installation requests or system password prompts.
Read the full analysis 👇
Show more


🚀 SlowMist has officially released MistEye DNS Guard, a lightweight local DNS relay and threat observation tool built with Rust for macOS and Linux.
By turning DNS into an observation point, MistEye DNS Guard helps detect malicious domains, public IPs, and outbound process connections — while keeping normal DNS resolution unaffected through asynchronous threat detection.
🌟 Key capabilities:
🔹DNS relay & system DNS takeover
🔹Domain and public IP threat detection
🔹Outbound process monitoring
🔹Malicious event retention & Webhook alerts
🔹Lightweight deployment with built-in SQLite persistence, no external database required
⚡ No complex infrastructure required — download the precompiled binary, configure the TOML file, and start monitoring.
📄 Learn more about MistEye DNS Guard:
🛠️ Explore the open-source project:
Show more


🚨SlowMist TI Alert🚨
💸 @LienFinance Loss: ~542k USD
🔍 Root Cause: The `exchangeEquivalentBonds` function in BondMakerCollateralizedEth lacks proper multiset integrity checks. It only counts total exception occurrences instead of verifying each bondID's appearance per group. By repeating a single exception bondID in the output group, attackers consumed the exception count twice, masking a missing input exception. This allowed minting new non-exception BondTokens without burning the corresponding input bonds, which were then sold for USDC from a pre-approved victim address.
📌 Attacker: 0x0d7d9023531ad1a88414e216ee2715f63561808a
📌 Victim: 0xa961684a3a654fb2cca8f8991226c0cefc514d80
📌 Vulnerable Contract: 0xda6fc5625e617bb92f5359921d43321cebc6bef0, 0x843225cf6e663e4454732d6b551a737ac7b47de0
Attackers exploited the flawed exception-counting logic to mint unbacked bond tokens, swapped them for USDC via three pre-authorized endpoints, and drained 542,144.628604 USDC from the victim.
Powered by
Tx:
Show more
🚨 SlowMist TI Alert 🚨
💸 @VerusCoin Loss: ~$7.5M
⚠️ Unlike the prior 0x6990…b321 exploit, which decoupled the validated proof from the executed transfer payload, this attack hash-bound the transfers to the CCE but failed to validate the CCE’s economic backing; both exploit flawed cross-chain import validation.
🔍 Root Cause: `VerusProof.checkExportAndTransfers` verified selected CCE fields—including `hashReserveTransfers` against attacker-supplied serialized transfers and the source/destination IDs—but did not enforce the CCE’s accounting semantics. It failed to parse or validate `totalamounts`, `totalfees`, `totalburned`, CTxOut `nValue`, or whether the prior CCE outpoint carried sufficient value and assets to cover the claimed transfers. As a result, a matching transfer hash was incorrectly treated as authorization to release bridge assets, rather than merely a commitment to the requested transfers.
📌 Attacker EOA: 0xbda71b58cec0b1c20a8f87ccd52fa0679747855c
📌 Victim Bridge: 0x71518580f36feceffe0721f06ba4703218cd7f63
📌 Vulnerable Contract: 0x54e03a1682fd0bb065b669f6296f97028dcfd4ce
📌 Fund Receiver: 0xcfd0a20703cd11e0b9f665e1c3f1ef989c142d54
Impact: The attacker submitted a successor CCE anchored to an accepted Verus state root, containing a hash commitment to eight attacker-defined reserve transfers. Because the bridge did not verify whether the CCE’s economic fields backed those transfers, it executed eight payouts from bridge custody to the attacker-controlled receiver—releasing ETH, DAI, USDC, USDT, and four additional tokens without enforced cross-chain asset backing.
Powered by
Tx:
Show more
🚨 Threat Intelligence | On-Chain Backdoor in a Malicious TRAE Extension
Following @Will42W’s warning about TRAE IDE extension supply chain risks, SlowMist investigated the malicious extension juannegro.solidity.
Although removed from Open VSX, the extension was still available through the TRAE marketplace as of July 18, 2026. It impersonated a legitimate Solidity plugin and acted as a cross-platform malware dropper.
Our analysis found that it:
🔹 Impersonates a legitimate Solidity extension and uses the marketplace as the initial malware delivery channel
🔹 Automatically executes after IDE startup and establishes persistence across platforms
🔹 Uses an Ethereum smart contract to store and retrieve dynamic C2 configurations
🔹 Allows attackers to update C2 endpoints and payload delivery without republishing the extension
This incident highlights how extension marketplaces can become initial infection vectors, while blockchain infrastructure can be abused for dynamic C2 management.
Users who installed juannegro.solidity should remove the extension and check their systems for potential compromise.
Full analysis👇
Show more


As Kimi K3 launches, check out our earlier podcast interview with Yang Zhilin, founder of Kimi. We recorded it right after K2 came out, and so much has changed over the past year.
Show more

🚨 Threat Intelligence | Fake Recruitment Campaign Delivers Malware via GitHub Repository
MistEye recently detected a malicious campaign targeting developers through fake Web3 recruitment.
Attackers impersonated recruiters on LinkedIn, built trust through discussions about work experience and interviews, then sent a GitHub repository disguised as an “interview MVP” and tricked developers into running the project.
Our analysis found that the malicious repository hid theme/js/auron-core.min.js as a Tailwind plugin. When developers ran the project’s development or build commands, the hidden Node.js loader was triggered and deployed multiple payloads for:
🔹 Browser credential & wallet data theft
🔹 Sensitive file collection and exfiltration
🔹 Remote command execution and interactive Shell access
🔹 Clipboard monitoring
This campaign shows how trusted development workflows can become attack vectors. Developers should always inspect project scripts, dependencies, and build configurations before running unknown repositories.
Full analysis👇
Show more


xAI the response:
“Reports focusing solely on client side issues on grok-build-cli are considered out of scope.” 🙂↕️
Previously, we analyzed Grok CLI’s data upload behavior and found that its repository upload mechanism could send git bundles containing sensitive files such as .env files and RSA private keys.
Following that analysis, we continued auditing Grok Build CLI’s security model after it was open-sourced.
Within 24 hours, we identified two attack chains that can lead to arbitrary code execution without explicit user approval.
The root cause is not a single bug, but a fragmented trust model: project-level files can influence AI Agent instructions and permission decisions without sufficient validation.
Key findings:
🔹 cargo check was incorrectly classified as a safe command. Combined with malicious AGENTS.md instructions, attackers can trigger execution and achieve code execution.
🔹 .claude/settings.json with bypassPermissions can override permission checks and enable unrestricted tool execution.
🔹 Grok Build CLI inherits Claude Code CLI’s permission configuration model, exposing similar risks.
🔹 .mcp.json introduces additional project-level attack surfaces through MCP configuration.
These findings highlight a broader issue:
When #AI# coding agents trust project-level files too much, opening a project can become equivalent to granting shell access.
📖 Full technical analysis:
👉 Previous analysis:
Show more











