

Sani | TimechainIndex.com
@SaniExp
Founder | Timechain Archmage | ₿ Addresses Labeling Services | Lightning Donations: sani@blink.sv
636 Following 18.2K Followers
Funds were sent to new MetaPlanet addresses, total still 43,000 BTC
Bitcoin miner Metaplanet (@Metaplanet), which bought 43,000 ($3.48B) at an average price of $96,191, deposited another 2,400 ($186M) into Coinbase Prime in the past 3 hours.
Show more


Who’d be interested in a limited-edition “Seed Round” of EntropyLab merch to help fund our clankers for the next few weeks/months?
I’m thinking a small run of a few different items...just 21 of each, individually numbered and tastefully branded with the EntropyLab logo.
Each piece would be marked:
Seed Round · x/21
Show more


Can everyone calm their tits for the next 10 days until i get the fuck out of this part of the world 😭

🇮🇷🇸🇦 Air traffic has been temporarily halted in Jeddah, Saudi Arabia, as the latest Iranian missile activity unfolds across the region.
Another sign that tonight’s escalation is being felt far beyond the targets themselves.
Source: @officialrnintel on TG / Writer: Oliver
Show more

6 Casascius Coins on the loose, most likely belonging to 1 or 2 people

Schrödinger's Coldcard
Your keys might be your and not yours at the same time

There are 3 really simple things you can do to protect yourself against 90% of social engineering attempts. Most of these operations are casting a big net and just trying to scoop up unsuspecting fish. So make yourself a slightly harder target and they will pass right over you.
1. Don’t ever answer the phone for unknown numbers. Even when the location says Mountain View, CA, or the caller ID says Google. It’s fake! To ensure you don’t get tricked, set your phone setting to Silence unknown numbers automatically. On iPhone it’s Settings ➡️ Phone ➡️ Screen Unknown Callers ➡️ Silence (see screenshot). Many times, bad actors are using fear over the phone to get you to do things you shouldn't - like give them control of your email.
2. Add 2FA to your main email account, and make sure it uses a unique, strong password. Use either an authenticator app or a Yubikey (better) as your 2FA. ➡️ Security & sign-in ➡️ Turn on 2-step verification. Then make sure your password is a unique password that isn't used anywhere else. If you are using the same password in more than one place, it's highly likely that it's been leaked. Just go to put in your email address, and look at how many leaks its been in.
3. If you use Google Authenticator, turn off the cloud sync. When you have cloud sync on, if someone compromises your Google account, they can steal your 2FA. It makes 2FA ➡️ 1FA, and that is bad.
These are the basics that you can do to protect yourself against a huge amount of social engineering. And then if you want extra protection for your BTC, check out the next post 👇
Show more


Over 10k BTC from multisig wallets have now been submitted through slipstream since the coldcard weak seed thefts began.
By doing this a previously concealed witness script can remain private until the transaction confirms, avoiding the risk of theft.
Show more

CleanSpark sent 5,000 BTC to Coinbase Prime


📊 updated numbers on coldcard exploit
8865 addresses lost 1789.28 BTC worth $114.7m at the time of theft ($138.8m today)
- loss by address
median 0.00152
mean 0.20184
dormancy median 3.2yr
dormancy mean 3.6yr
- loss by victim reports (221)
median 1.04272
mean 3.57792
dormancy median 3.25yr
dormancy mean 2.99yr
victim reported loss 790.72 (44.2% of total)
if we expand to include medium confidence losses (not yet confirmed) the total loss is 1,824 BTC ($140m at the time of loss)
Show more

As of Saturday 08/22/2026, 23:33:47 UTC, centralized exchanges held a total of 3,699,324 BTC, smashing through another reserves ATH and adding 193,726 BTC YTD.
Exchanges balances increased by a net of 5,980 BTC this week, while ETFs/ETPs added 23,908 BTC during the same period.
Show more

As of Saturday 08/08/2026, 23:44:08 UTC, centralized exchanges held a total of 3,683,123 BTC.


Signs you don’t understand Bitcoin:
You have a collaborative custody.
Bitcoin's white paper suggests and I quote:
''A purely peer-to-peer version of electronic cash would allow online payments to be sent directly from one party to another without going through a financial institution.''
Show more
And ETFs


On August 6th, the Bitcoin Red Team sent us a report on AQUA. Around the same time, reports were coming in from independent researchers, and we'd been running our own scans across the codebase using frontier AI models.
Between the three, one high-priority issue surfaced. It was theoretical, and it sat in an experimental feature for sweeping Bitcoin and Tether poker chips. That feature sees very limited usage and handles small amounts. It has been patched.
We found no issues with seed entropy, and none pertaining to the core AQUA wallet and services. A handful of minor items came out of the review, none urgent, and they're queued for upcoming releases.
The caveat we'll keep repeating regardless: AQUA is a hot wallet. Hot wallets carry inherent risk by design. If you're holding large amounts for the long term, use cold storage.
Many thanks to the Bitcoin Red Team, to the researchers who filed reports, and to everyone who takes the time to tell us when something looks wrong. Bitcoin gets safer because people do this. 🐬
Show more
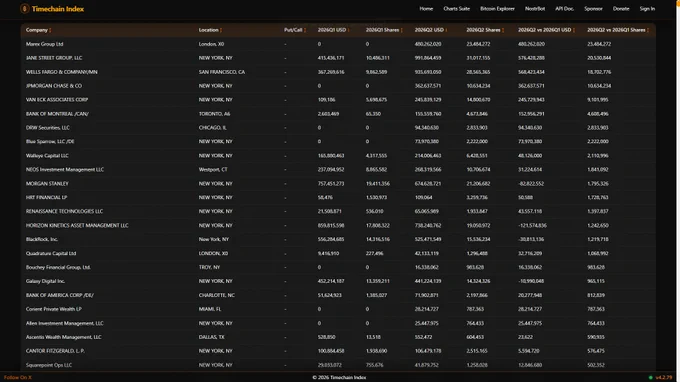
As of Friday, August 14, 1,896 institutions reported holding a combined $17.1 billion worth of Bitcoin ETF shares in their Q2 2026 13F filings.
Across all Bitcoin ETFs, reporting institutions disclosed a net increase of 58.1 million shares compared with Q1 2026.
For a full breakdown of institutional holdings, quarter-over-quarter changes, and individual Bitcoin ETFs, explore the data on Timechain Index’s 13F Bitcoin ETF Overview at:
Show more

What a mess. Unfortunately this Trezor address leak will directly lead to an increase in targeted social engineering and potentially wrench attacks. Here are my recommendations for what to do if you were in this breach (or just want to protect yourself against the result of these breaches in the future).
Social engineering protection
Scammers will use the combination of having your personal information to both target you (phone, email) and convince you that they are legit (using your name and potentially home address as proof that they know you and are here to help).
They will contact you via phone or email with targeted lies meant to scare you into talking to them and taking the actions they want you to, in the name of protecting your bitcoin. Ignore any communication from "Trezor" that doesn't come from their official domains (the @Trezor handle, are the main ones I know of).
You should also ignore communication from "Google" or "Apple" pretending like your email is compromised. They trick you into giving them your email credentials, and then once inside your inbox they can do all manner of things to trick you without Google's typical filters stopping them.
Generally a company's support team will never call you on the phone without you contacting them. If they reach out proactively and are trying to get you to take any action to "remain safe" - refuse.
Social engineers steal much more money on a regular basis than physical attackers. Most people worry about physical attack more because it sounds scarier, but the bigger risk of actual funds loss is social engineering. Get your suspicion antennae up.
Phishing
Phishing has a lot of overlap with social engineering. The main difference in my mind is that phishers put in less effort than social engineers. Social engineers may use phishing tools to help them. Phishers are just putting their nets out and trying to get you to make a mistake.
Be very suspicious of emails directing you to go to Trezor's website or download a new Trezor app. Triple check the URL for Trezor or any hardware wallet website that you visit. Even if you Google Trezor, there are fake Trezor phishing apps running Google ads that will tell you to type in your seed phrase and then steal your money. Be very careful when downloading or using new wallet apps that you are getting the right one.
Wrench attacks
The one everyone worries about the most, even though it's the least common. Unfortunately since this breach includes physical addresses, it's possible we will see some wrench attack attempts come from it. Unless you are going to move, the best you can do is try to deter attackers and make sure that if it happens, they can't steal all your money.
Distribute your keys and use a multisig to ensure that you don't have enough keys to spend bitcoin at your house. Then consider keeping a small-ish amount of BTC in a single sig wallet that you are willing to give up to make someone go away.
We don't recommend the type of duress wallet that uses the same device/software as your main wallet, but when you type in a different PIN it brings up the fake wallet. It's too hard to remember the duress PIN when someone is beating you up, and too easy to give in when they ask you for more after you pay them from the duress wallet. You need to make it so you truly can't send them all your money.
Casa recently built Guardian Mode to help protect against social engineering and wrench attacks. It requires the Casa key to sign for all transactions you send. We do a video verification call to make sure you are not being tricked or under duress before signing with our key. Available to Premium+ Casa members.
You can also check out an old post we did about physical home security, which unfortunately we have to reshare every year or two:
Very sorry to all the people who were caught up in this. Rough few weeks for bitcoin security. Reach out to us if you need assistance on any of these points.
Show more

A big thank you to @JoelBomgar for generously sending me $250 to get a Bitkey, and for sending sats to over 100 other users to help them get their own Bitkey as well.
With Joel’s consent, I’ve donated the $250 to the Bitcoin Arabia team @Bitcoin21_ar so they can get a Bitkey, review it, and create Arabic tutorials for our Arab Bitcoin community.
Thank you, Joel, for your generosity ❤️
Show more

TimechainIndex wouldn’t exist without @mempool. Forever grateful for everything you legends have built 🫡🫡🫡

Periodic reminder that @mempool is hands down one of the coolest companies in Bitcoin.
I use them daily and can't thank them enough for existing. 🙏
As of Saturday 08/08/2026, 23:44:08 UTC, centralized exchanges held a total of 3,683,123 BTC.
I highly recommend reaching out to @Thebitcoinway_ for professional assistance.
They can help you address the current situation and reduce the risk of similar issues in the future.

🚨 COLDCARD VULNERABILITY UPDATE 🚨
A quick update based on the info we have so far.
Watch this video to understand:
- What happened
- How you should respond
- What happens next
Remember to stay calm and avoid rash decisions
If you need help, reach out to us @Thebitcoinway_ for support.
Show more

Run your own node people 😂😂

1/ During our investigation of the Coldcard drain yesterday, we identified an unusual pattern in the sweeps. That pattern led us to a hypothesis that has since been confirmed: the operator used a paid account at a well-known blockchain-services provider to query the source addresses and perform other related activity during the sweeps.
Show more












