
Cos(余弦)😶🌫️
@evilcos
Founder of @SlowMist_Team // 分身一号/捉虫大师/救火运动员 // 🕖灾备频道
1.6K Following 127.5K Followers
I don’t think THORChain’s TSS + validator model represents true decentralization.
The selected validators set collectively controls the underlying assets in the TSS vaults. Once the signing threshold is reached, those validators can move the funds. So from a custody perspective, THORChain is not comparable to Bitcoin or Ethereum base-layer consensus — it effectively acts as an intermediary between users and the native chains.
TSS distributes control among multiple parties, but distributing an intermediary does not eliminate the intermediary.
Show more

Tether banned the wallet owned by the bitget exploiter

🚨 Unauthorized NFT transfers observed via Limit Break's Payment Processor on Ethereum and ApeChain.
If you've approved Payment Processor on any chain, revoke it as a precaution. Cancelling listings doesn't remove the approval.
V2: 0x9A1D00bEd7CD04BCDA516d721A596eb22Aac6834
V3: 0x9a1d00000000fc540e2000560054812452eb5366
Per @0xQuit, NFTs in 0x71cF3f5724bD2B72Ef6464992aCd26216DE7fe33 are held by a whitehat and expected to be returned.
Show more


We’re working closely with @bitget on the ongoing investigation. For further details, please refer to Bitget’s official updates.

[UPDATES] We are currently working with independent third-party experts Mandiant and SlowMist for a full investigation.
Our first priority is our users. User balances remain intact, and Bitget's User Protection Fund covers the impact on this platform-wide incident.
Bitget Wallet operates as a self-custodial wallet on a completely separate and independent infrastructure from Bitget Exchange and was not affected by this incident.
Bitget Wallet users' assets remain onchain under users' control and remain unaffected.
The Bitget Exchange platform continues to operate normally.
Withdrawals are still temporarily paused while we complete additional security checks, and we will restore them as soon as we are confident that it is safe to do so.
We know that during an incident like this, users want answers quickly. We will provide timely updates through Bitget's official channels.
Show more
So far, we have identified the following addresses associated with the @bitget exploiter that still hold funds. We will continue to update this list. @GracyBitget @xiejiayinBitget @Bitget_zh
Show more

All hacker addresses have been tagged. We’re actively monitoring fund transfers and expanding our blacklist. We remain fully committed to combating illicit transactions.
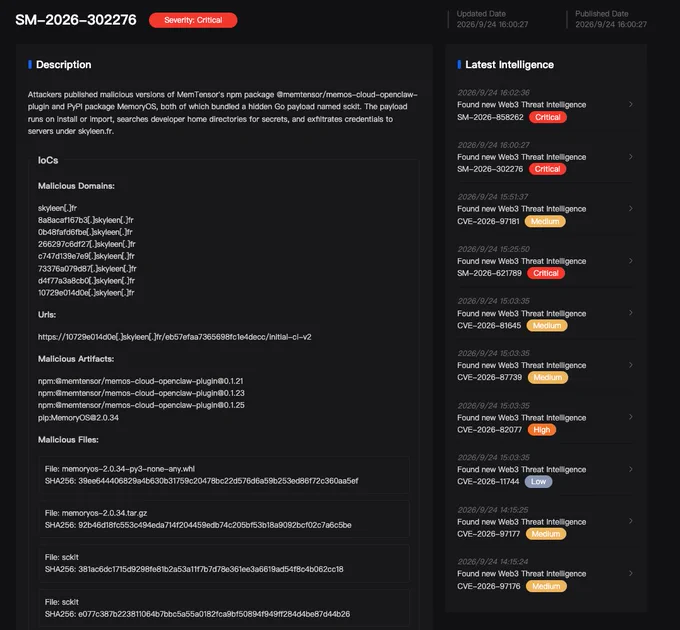
🚨 SlowMist TI Alert 🚨
MemTensor's AI memory tooling has been compromised: MemoryOS (PyPI), the company's open-source long-term memory library for LLM and AI agents, and memtensor/memos-cloud-openclaw-plugin (npm), the official plugin connecting it to the OpenClaw agent runtime.
Affected versions bundle cross-platform Go binaries that execute when the package is loaded or imported: MemoryOS==2.0.34 on PyPI, and plugin versions 0.1.21, 0.1.23 and 0.1.25 on npm. You are affected if the PyPI version has been imported in your environment, or if the npm plugin is installed and the OpenClaw gateway has been started.
Potential attacker actions include harvesting npm/PyPI tokens, GitHub/GitLab credentials, AWS keys, SSH keys, API tokens, environment secrets, and other developer credentials, with data sent to infrastructure under skyleen[.]fr. The affected npm plugin may also expose user prompt content.
Users should remove or downgrade affected packages to known-good versions (0.1.20 for npm and 2.0.33 for PyPI), terminate sckit processes, block associated infrastructure, review network activity, and rotate credentials accessible from affected environments.
You can also visit to check for free whether the npm packages, pip packages, domains, or IPs you use are safe.
Reference:
As always, stay vigilant!
Show more
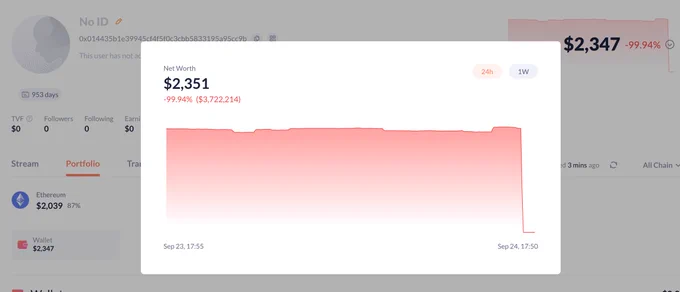
🚨 Duelbits hot wallets on Ethereum, BSC and Tron saw ~$4.2M in outflows to newly created addresses, in a suspected private key compromise.
Assets moved included 836 ETH, 1.62M USDT, 97K USDC, 209 BNB and 192K TRX. Most have since been swapped to ETH.
Duelbits (EVM): 0x014435b1e39945cf4f5f0c3cbb5833195a95cc9b
Duelbits (Tron): THqFmhAPcdHECH3wmrpZv4MWAB2v9TY1oN
Hacker (EVM): 0xa77e24fe29d16e051e487ef4ea7b056cb05aef76
Hacker (Tron): TAvraZZFCZbDSZoyqWWRRsBkFgZqKaCGbK
Show more
Thanks to @Cointelegraph for covering our investigation into the FomoPeek App Store poisoning and iOS kernel exploitation, conducted together with the @wallet security team. 🫡
We appreciate the opportunity to share our findings and help users better understand the risks and recommended response. 🌟
Read more 👉:
Show more


‼️ BREAKING: An app on Apple's official App Store was serving iPhone users malware designed to steal crypto wallet keys.
SlowMist and OKX found FomoPeek versions 1.1 and 1.2, distributed Sept 9–17, hid a kernel exploit framework built to escape the iOS sandbox, decrypt the Keychain and pull data from 19 apps, including MetaMask, Trust Wallet and Apple Notes.
SlowMist traced nearly 580,000 USDT to the attacker's main wallet.
Show more


⚠️ Security Alert: FomoPeek v1.1-1.2
A joint investigation by our security team and @SlowMist_Team has found malicious code in FomoPeek App versions 1.1–1.2 that may expose private keys, seed phrases, credentials, and other sensitive data on iOS devices.
If you've installed or used these versions:
• Stop using FomoPeek immediately
• Create a new wallet with new keys on a trusted device where FomoPeek was never installed
• Transfer your assets to the new wallet as soon as possible
• Update iOS to the latest available version
• Check your accounts for suspicious activity
If you detect unauthorized activity, contact the relevant platform's official support team and retain the affected device and evidence for investigation.
Protect your keys. Stay vigilant.
Show more

🚨SlowMist TI Alert🚨
💸 @Fetch_ai Loss: ~$2M
🔍 Root Cause: TokenConversionManagerV3's conversionIn() leaves single-EOA ECDSA signature as the sole authorization check. It lacks the checkLimits(amount) modifier present in conversionOut(), and does not verify any on-chain burn/lock proof. Using the leaked authorizer private key, the attacker signed a fresh message for their own address, passed the check, and drained the bridge's entire FET balance in one call.
📌 Attacker: 0x1572f2af7696b39c85e3221cde8efb640f86c362
📌 Recipient: 0x2dcc1085fdcf418b421e45e86e4e54637cc21dfe
📌 Victim/Vulnerable Contract: 0xab424a430cc09864fa1277a38193111705adf3a3
Powered by
Tx:
Show more

⚠️ Security Advisory | iPhone Users: Check Whether You’ve Ever Installed the FomoPeek App
Binance is aware of a security incident recently disclosed by the community. According to security firms including SlowMist, the third-party app FomoPeek (versions 1.1–1.2) contains malicious code that can exploit iOS system vulnerabilities to gain the highest level of device privileges, potentially accessing sensitive data stored on the device, including private keys, seed phrases, login credentials, chat history, files, and more.
Please note that this type of malware targets the device itself. If an attack succeeds, data from all apps on the affected device may be accessed.
Please check the following:
1. Are you using an iPhone or iPad running iOS 26.x or earlier?
2. Have you ever installed the FomoPeek app?
If both apply to you, we recommend taking the following steps immediately:
1. Delete the FomoPeek app and do not reinstall it.
2. Update your iOS to the latest available version.
3. For self-custody wallet users: On a device that has never had the app installed, create a new wallet and transfer your assets to the new wallet address.
4. If you notice any unusual asset activity, preserve the affected device and relevant evidence, and contact Binance Customer Support for further investigation.
We also remind all users: Do not install apps from untrusted sources, and keep your device software up to date.
Show more

🚨SlowMist TI Alert🚨
💸 @likwid_fi Loss: 74.31 BNB
🔍 Root Cause: LikwidMarginPosition._executeAddCollateralAndBorrow (leverage=0 branch) never assigns delta.pairDelta, so the borrow path leaves pairReserves untouched. getAmountOut(pairReserves,...) returns the same 4.7857 BNB quote on every call — the attacker repeated the margin/borrow cycle 14 times, settling 211.8M TOKEN at the first-trade marginal price with no AMM price impact.
📌 Attacker EOA: 0x90bde1e0bb16b3deeb9d638acf8d01f19fd2f31e
📌 Attack Contract: 0xc63fb27f52ed8d06673c60c3075b2d3bd26cf4aa
📌 Vulnerable Contract: 0x6bec0c1dc4898484b7f094566ddf8bc82ed7abe8 (LikwidMarginPosition)
📌 Victim Contract: 0x065d449ec9d139740343990b7e1cf05fa830e4ba (LikwidVault)
Powered by
Tx:
Show more
🚨 SlowMist TI Alert 🚨
@DCENTWALLETS has reported abnormal asset transfers involving its App Wallet. Users should update the DCENT app to the latest version before making any transfers.
Stay alert for #phishing# and impersonation attempts. Never share your recovery phrase/private key or send assets to any address for “recovery” or “compensation.”
Please refer to DCENT’s official announcement for details and further updates.
Show more

Important Update Regarding the DCENT App Wallet
To date, abnormal asset transfer cases have been identified involving the DCENT App Wallet. So far, we have not confirmed any impact originating from DCENT Hardware Wallets themselves.
Please follow the guidance below based on how you use the DCENT app.
If you hold assets in the DCENT App Wallet, or if the same recovery phrase is used for both your DCENT App Wallet and a hardware wallet:
Please update the DCENT app to the latest version before transferring any assets to a secure hardware wallet or another trusted wallet address.
• Update the DCENT app before transferring any assets.
• Do not initiate transactions through the DCENT App Wallet before updating the app.
• If the same recovery phrase is used in the DCENT App Wallet, action is required regardless of where that recovery phrase was originally generated.
If you only use your DCENT Hardware Wallet with the DCENT app:
No additional action is required for your hardware wallet if you have never entered or restored that hardware wallet’s recovery phrase in the DCENT App Wallet.
⚠️ Please remain vigilant against impersonation and phishing attempts.
• DCENT will never ask for your recovery phrase or private key, nor will we ask you to send assets to a separate wallet address for recovery or compensation.
• Do not follow recovery or compensation instructions, wallet addresses, or links sent through DMs, email, social media, or other unofficial channels.
We are prioritizing the investigation into the related cases and will provide further updates through our official channels as soon as the cause, scope of impact, and additional response measures are confirmed.
Official X accounts (We have no support X accounts)
@DCENTWALLETS
@DCENTWALLETS_KR
@DCENTWALLETS_JP
Customer Support
Show more

🚨SlowMist TI Alert🚨
💸 Unknown Gnosis Safe wallet Loss: ~$7.73M
🔍 Root Cause: In the `multicall(address, bytes[])` function of the Router contract (address `0x4f005592…`), the `_contract` parameter could be set to `address(this)`. Consequently, the `_isAuthorized` function—used for internal permission checks—would unconditionally return true. This allowed the victim Safe module contract to execute attacker-crafted malicious call data via `DelegateCall`, injecting aEthrsETH into an attacker-created liquidity pool equipped with a hook; the assets were subsequently swapped and redeemed for profit.
📌 Attacker: 0x2f7e143e27f2fa26ef3b8ac72698f1d321422f67
📌 Victim: 0x40e93a52f6af9fcd3b476aedadd7feabd9f7aba8
📌 Vulnerable Contract: 0x4f0055926c839d1d960a82cbf84e2ee933958ebc
Txs:
Powered by
Show more

🚨 On September 6, 2026, @Liquid_BTC was affected by a cache key collision vulnerability in rangeproof verification.
An attacker minted ~3,998.5 L-BTC with no corresponding peg-in. Within minutes, the unbacked L-BTC was pegged out into real BTC on the Bitcoin mainnet. About 3,400 BTC was later returned to the federation peg wallet, while ~598.5 BTC remains under the attacker’s control.
The SlowMist Security Team traced the fund flows on the #Bitcoin# side using @MistTrack_io and fully analyzed the incident.
🧩 Attack flow:
1️⃣ Two setup transactions first landed valid rangeproofs and commitments, while embedding a crafted payload in the locking script to seed node caches.
2️⃣ A follow-up minting output reused a colliding cache key — the same raw concatenation of proof, commitment, asset commitment, and scriptPubKey, but with different field boundaries.
3️⃣ On a cache hit, nodes skipped secp256k1_rangeproof_verify and min-value checks, accepted an unbacked commitment, and minted ~3,998.5 L-BTC. The fake UTXOs were consolidated and pegged out within minutes.
⚙️ Root Cause: The Elements rangeproof cache key concatenated variable-length fields without length prefixes. Distinct argument tuples could hash to the same key, so a positive cache hit meant skipping cryptographic verification.
🛡️ SlowMist Insight: A positive-result cache in a consensus verification path is itself a cryptographic primitive. Every field the verifier reads — and every field boundary — must be unambiguously bound into the key. Treat cache-key integrity as a mandatory item in consensus-layer audits.
Full analysis👇
Show more


🚨SlowMist TI Alert🚨
We first reached out to the team privately to responsibly disclose the issue before making any public statement.
💸 @ether_fi Loss: ~15.45 ETH
🔍 Root Cause: `AtomicQueue.solve()` lacks access control on the caller-supplied `solver` — there is no `solver == msg.sender` check, nor any signature, registration, or consent verification. The attacker first created a maliciously crafted `AtomicRequest` using the `updateAtomicRequest()` function, then forced a victim address to act as the `solver`. AtomicQueue subsequently called `finishSolve` on the victim and executed `want.transferFrom(solver, users[i], assetsToUser)`, abusing the victim's pre-existing ERC-20 allowance to drain funds.
📌 Attacker: `0xa5cc6e490bce9185fa47b421f2eac677a83b64ea`
📌 Vulnerable Contract (AtomicQueue): `0xd45884b592e316eb816199615a95c182f75dea07`
Powered by
Tx:
Show more

🚨SlowMist TI Alert🚨
💸 @BeatXswap Loss: 2,984,557 BTX (~$77,512)
🔍 Root Cause: The `LiquidityVestingConvert` contract calculates BTX quotes via `_calculateQuote()`, which reads `IUniswapV3Pool.slot0()` spot price as the sole oracle. No TWAP protection, no sanity check, no deviation limit. An attacker borrowed 6,000,000 BTX via flash loan, dumped it into the V3 pool to crash `sqrtPriceX96`, then called `deposit()` twice (10,000 + 2,000 USDT), triggering `POSITION_MANAGER.mint()` at the manipulated spot price and draining BTX from LP positions.
📌 Attacker: 0x67B2f08683A735cfE6f6E57fA86909b62218C2a1
📌 Victim:
0x1e647FAADb05f2124BFCcFC003EDc06D1A90bf5D
0x9a7A92240FBAc4030b65A6E61239928d6Bcc716F
📌 Vulnerable Contract: 0x1e647FAADb05f2124BFCcFC003EDc06D1A90bf5D
Powered by
Tx:
Show more










