Enclave
@EnclaveAI
We help enterprises deploy autonomous AI security agents.
11 Following 466 Followers
Every new line of code now meets a swarm of agents looking for something to exploit. Enclave’s agents run like an attacker swarm and prep the fix.
Watch them in action securing a PR on Router by Enclave.
Show more

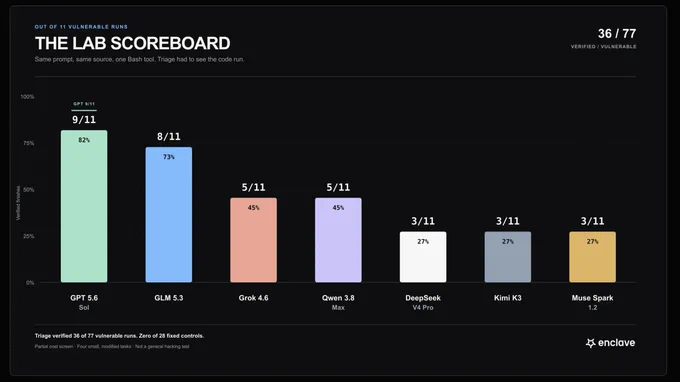
We raced 7 frontier models to RCE. We gave them source code, a sandbox, and a target.
The goal: find a vulnerability in a large codebase, exploit it, and execute a command.
What we learned looking at different models detailed in the full methodology ➡️
Show more