

Specter
@SpecterAnalyst
Onchain Investigator | Peace ✌️
Specteranalyst.sol (.eth)
463 Following 16.6K Followers
So far, $2.8B has been frozen. Shout-out to the teams for their swift action.
Next: First Digital should help freeze the remaining $3.45M in FDUSD.
Stay smart.

There have been a reports on X and Reddit of wallet-draining by Ledger users.
I traced the theft addresses and identified inflows from more hundreds of victim wallets across several major blockchains, including Ethereum, TRON, and Bitcoin.
Total losses $86M+
bc1qjqgwejnp8dc0x2938x9n9954hj97t82unx49dl
TK6DWNpNe1w2iJRNFpU8aHdrPTATxvXT6C
TBkcUMYC7CkTK99tkTnaStQVBastfrs9d9
TCGE3xp6YGRKXxDZiLfysgJW3f22KfMNsW
0x69c8f401cfc6cd40ac94691d6d7c48e3b7a47841
0x033636e45d519bebb7b5c2520ca6ce56fbdb4f7a
0x83aeac166f6832ae3500000a24510a95a052a599
bc1qqnkwurxs99xkx5t4yffqhq3u6qwy0qpjyujtm9
bc1qgqheemzla77pesl227hdtgf5ykz62d0zvld26n
TSDWtuZ2pARUVz4v3PkL2hi3iXPjowAr5a
Show more


I spent about 13 minutes reading this, and I must say, this is incredible. Just imagine the amount of risk involved and the money spent throughout this investigation.
I hope Jimmy gets what he deserves, and that his fat-reducing meals are served with plenty of water in prison.
Great job, ser. 👏
Show more


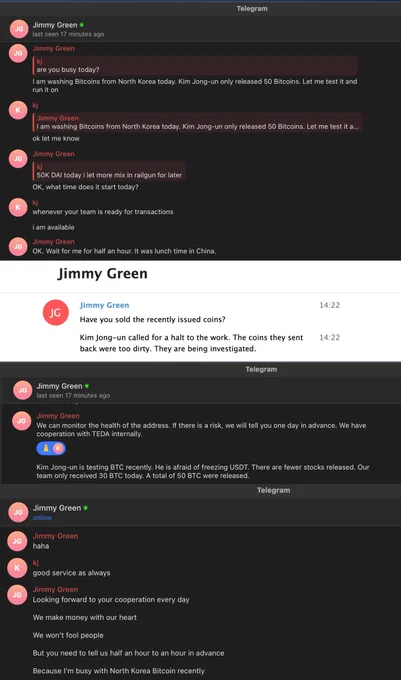
1/ How I infiltrated a Chinese organized crime syndicate that has laundered $1B+ across multiple exploits for Lazarus Group.
Posing as a client, I gathered intel that helped action freezes for the Feb 2025 Bybit exploit and attribute illicit activity onchain.
Show more

I spent about 13 minutes reading this, and I must say, this is incredible. Just imagine the amount of risk involved and the money spent throughout this investigation.
I hope Jimmy gets what he deserves, and that his fat-reducing meals are served with plenty of water in prison.
Great job, ser. 👏
Show more
1/ How I infiltrated a Chinese organized crime syndicate that has laundered $1B+ across multiple exploits for Lazarus Group.
Posing as a client, I gathered intel that helped action freezes for the Feb 2025 Bybit exploit and attribute illicit activity onchain.
Show more
I also contributed to freezing of 173k XRP ($257K) via near intents (yet to be awarded to me)
Thanks to near team for swift action


If there was no THORChain, shit would be hell for these guys😑.
They’re laundering funds across several chains, even on bottom chains like dYdX, Noble, and Osmosis. So annoying.
How stupid can you be to publicly post txs link of stolen funds that are being tracked by the public? very soon....
Show more
BREAKING: Chinese illicit actors laundering funds from the $387M Bitget exploit on behalf of the alleged DPRK attackers are openly asking for support with orders in public Discord servers and Telegram channels of services they use.
Notably, Alias 4 (below) was also seen laundering funds from the Kelp DAO $292M exploit earlier this year.
I've observed the same pattern after multiple TraderTraitor attributed exploits, and I've closely tracked these groups. I plan to share more of my data on them in coming weeks.
Currently, funds are being chain-hopped via bridges and being deposited into mixing services such as Wasabi.
Alias 1 - Cc
Discord: cc02006
Discord ID: 1351486674386948148
Txn: F08657EFAEAE7B58217CD17A22BF4779582E5D080C2E92E173BC239A5D828363
Alias 2 - jack
Discord: jack_34808
Discord ID: 1553705721768714377
Txn: 68583D313A0CCC99F2702D61D05A242A69C86CAE09ED252B65F34B677C377F69
Alias 3 - Melon
Discord: under0346
Discord ID: 1394240539108573215
Txn 1: ABE2AEF8B10057E60F8259CA2CA2CD5D71D38D254960FEEE89CB3C95A964873F
Txn 2: 7BE290865901DEB1680A6D692A11392D1FDDACA0D31C48F26DCB249F2444BD6B
Alias 4 - lolo / Marin
TG: pvpcz
TGID: 6223514198
Discord: losern
Discord ID: 1024415186527985704
Txn: 8E935C19D00F40639B78BF1FD094FE48C92118F3E586AB52DF93851080CCCE15
Alias 5 - HELP ME
Discord: helpme031897
Discord ID: 1554035533817188384
Txn: 7C58CAD760EBBED54F2CA4D2146D056910B7B6688B4F524396DC8807353C2379
Show more


If there was no THORChain, shit would be hell for these guys😑.
They’re laundering funds across several chains, even on bottom chains like dYdX, Noble, and Osmosis. So annoying.
How stupid can you be to publicly post txs link of stolen funds that are being tracked by the public? very soon....
Show more
BREAKING: Chinese illicit actors laundering funds from the $387M Bitget exploit on behalf of the alleged DPRK attackers are openly asking for support with orders in public Discord servers and Telegram channels of services they use.
Notably, Alias 4 (below) was also seen laundering funds from the Kelp DAO $292M exploit earlier this year.
I've observed the same pattern after multiple TraderTraitor attributed exploits, and I've closely tracked these groups. I plan to share more of my data on them in coming weeks.
Currently, funds are being chain-hopped via bridges and being deposited into mixing services such as Wasabi.
Alias 1 - Cc
Discord: cc02006
Discord ID: 1351486674386948148
Txn: F08657EFAEAE7B58217CD17A22BF4779582E5D080C2E92E173BC239A5D828363
Alias 2 - jack
Discord: jack_34808
Discord ID: 1553705721768714377
Txn: 68583D313A0CCC99F2702D61D05A242A69C86CAE09ED252B65F34B677C377F69
Alias 3 - Melon
Discord: under0346
Discord ID: 1394240539108573215
Txn 1: ABE2AEF8B10057E60F8259CA2CA2CD5D71D38D254960FEEE89CB3C95A964873F
Txn 2: 7BE290865901DEB1680A6D692A11392D1FDDACA0D31C48F26DCB249F2444BD6B
Alias 4 - lolo / Marin
TG: pvpcz
TGID: 6223514198
Discord: losern
Discord ID: 1024415186527985704
Txn: 8E935C19D00F40639B78BF1FD094FE48C92118F3E586AB52DF93851080CCCE15
Alias 5 - HELP ME
Discord: helpme031897
Discord ID: 1554035533817188384
Txn: 7C58CAD760EBBED54F2CA4D2146D056910B7B6688B4F524396DC8807353C2379
Show more
BREAKING: Chinese illicit actors laundering funds from the $387M Bitget exploit on behalf of the alleged DPRK attackers are openly asking for support with orders in public Discord servers and Telegram channels of services they use.
Notably, Alias 4 (below) was also seen laundering funds from the Kelp DAO $292M exploit earlier this year.
I've observed the same pattern after multiple TraderTraitor attributed exploits, and I've closely tracked these groups. I plan to share more of my data on them in coming weeks.
Currently, funds are being chain-hopped via bridges and being deposited into mixing services such as Wasabi.
Alias 1 - Cc
Discord: cc02006
Discord ID: 1351486674386948148
Txn: F08657EFAEAE7B58217CD17A22BF4779582E5D080C2E92E173BC239A5D828363
Alias 2 - jack
Discord: jack_34808
Discord ID: 1553705721768714377
Txn: 68583D313A0CCC99F2702D61D05A242A69C86CAE09ED252B65F34B677C377F69
Alias 3 - Melon
Discord: under0346
Discord ID: 1394240539108573215
Txn 1: ABE2AEF8B10057E60F8259CA2CA2CD5D71D38D254960FEEE89CB3C95A964873F
Txn 2: 7BE290865901DEB1680A6D692A11392D1FDDACA0D31C48F26DCB249F2444BD6B
Alias 4 - lolo / Marin
TG: pvpcz
TGID: 6223514198
Discord: losern
Discord ID: 1024415186527985704
Txn: 8E935C19D00F40639B78BF1FD094FE48C92118F3E586AB52DF93851080CCCE15
Alias 5 - HELP ME
Discord: helpme031897
Discord ID: 1554035533817188384
Txn: 7C58CAD760EBBED54F2CA4D2146D056910B7B6688B4F524396DC8807353C2379
Show more

THORChain and Stolen Funds: The Industry Needs Answers
After the $1.46B @Bybit_Official hack last year, nearly $1.2B in stolen funds was reportedly traced through @THORChain as the attackers moved assets across chains.
Today, following another major security incident at @Bitget , we are once again observing Bitget Exploiter funds being sent into the THORChain for asset swaps and cross-chain transfers.
The question is no longer:
“Does THORChain know these funds are associated with hackers?”
The attacker addresses have already been publicly flagged and are being actively tracked by exchanges, blockchain security/aml firms, and the wider crypto industry.
The real question is:
When a protocol is aware that funds originate from a publicly identified major hack, yet continues to facilitate large-scale cross-chain swaps, how should the industry view this under the banner of “decentralization”?
Decentralization should not become a blanket excuse when dealing with known stolen funds.
If, after every major crypto hack, attackers can continue using THORChain as a route to move funds from ETH → BTC, BNB → BTC, and across other chains, the industry needs to seriously ask:
What responsibility should THORChain bear when handling known stolen funds?
@GracyBitget @xiejiayinBitget @benbybit
Show more
Regarding who is behind the hack:
I present to you THE LAZARUS GROUP.
just linked this hack to the AFX hack, which stole $24M in July and was specifically attributed to TraderTraitor.
The stolen XRP from Bitget was bridged and can be directly linked to the funds stolen in the AFX hack.
Stay smart.
Show more


The #1# reason you don't want to launder money for DPRK is that DPRK will absolutely hack you.
RIP Bitget. TraderTraitor says thank you for your service.
0xCbCfd64A96837D874943641fc9BA159C10d6CC80 -> 0xA0772d6E70D2c97CFB70628C7B00f666A6476feb
Show more

Regarding who is behind the hack:
I present to you THE LAZARUS GROUP.
just linked this hack to the AFX hack, which stole $24M in July and was specifically attributed to TraderTraitor.
The stolen XRP from Bitget was bridged and can be directly linked to the funds stolen in the AFX hack.
Stay smart.
Show more
Total loss: $353M
The remaining addresses
rwNhefsz1UQEusxhCvHip3RANinWi4CTck
rDRV9nLg8xbLsafKZnhNgWuE1TiSLE95hs
TBWNguTTgezw9dVorX441C6nDrZpRxYwKD

Where tf is bitget team @BitgetWallet @GracyBitget
Another $8.2M was just withdrawn on avalanche
Loss: 185M
Where tf is bitget team @BitgetWallet @GracyBitget
Another $8.2M was just withdrawn on avalanche
Loss: 185M
Crazy that I just realized this.
One of MetaMask’s swap router contracts was blacklisted by Tether in 2021 and remained blacklisted
I noticed the address was flagged while investigating the Payy Network hack.
Show more

Looking into this campaign, and I’d say proper research by victims could have prevented many of these losses. There were several red flags, but the promise of easy profits may have caused people to overlook them.
The threat actor(s) behind this campaign have drained $500K+ and appear to still be active.
I found a few of the YouTube videos used in the campaign, identified some of the theft addresses, and looked into how victims were being tricked.
One interesting part of the setup: the attackers registered ENS names containing “Uniswap,” making the addresses appear connected to legitimate DeFi activity:
0x331314385625D9912f8a5ee1bF86b837DCB42990
: uniswap-v3-router.eth
0x6E0CD1C8e1Df611E53E23B7900Ed8A830f4C871C
: uniswap-defi.eth
0x0E111ba687517937F08B189b84FbD02d86cbd739: uniswap-v2-pool.eth
These addresses were shown as sources of incoming transactions, making it look like contract were receiving profits from their deployed arbitrage trading bots via Uniswap.
But that wasn’t what was actually happening.
The attackers provided victims with a tutorial and code for creating the supposed arbitrage bot. The source code itself wasn’t the main trap.
The real trick was the development interface.
Victims were directed to an interface designed to look like Remix and instructed to use it to compile and deploy the contract.
After victims deployed the contract and funded it with their own assets, the attacker was able to drain the funds.
The attacker still appears to hold a significant portion of the stolen funds at these addresses:
0xcf27FAFb41e183C567E23786bB1f3E80a44b8Ef3
0x8d3736f31de511ad19c168973190a2e0c75f776a
Stay smart.
Show more


LATEST: 🚨 TRM Labs says 9 fake YouTube tutorials on building a crypto arbitrage bot with Claude tricked 224 victims into deploying self-draining smart contracts, netting scammers 274.60 ETH over 6 months.
Show more


Looking into this campaign, and I’d say proper research by victims could have prevented many of these losses. There were several red flags, but the promise of easy profits may have caused people to overlook them.
The threat actor(s) behind this campaign have drained $500K+ and appear to still be active.
I found a few of the YouTube videos used in the campaign, identified some of the theft addresses, and looked into how victims were being tricked.
One interesting part of the setup: the attackers registered ENS names containing “Uniswap,” making the addresses appear connected to legitimate DeFi activity:
0x331314385625D9912f8a5ee1bF86b837DCB42990
: uniswap-v3-router.eth
0x6E0CD1C8e1Df611E53E23B7900Ed8A830f4C871C
: uniswap-defi.eth
0x0E111ba687517937F08B189b84FbD02d86cbd739: uniswap-v2-pool.eth
These addresses were shown as sources of incoming transactions, making it look like contract were receiving profits from their deployed arbitrage trading bots via Uniswap.
But that wasn’t what was actually happening.
The attackers provided victims with a tutorial and code for creating the supposed arbitrage bot. The source code itself wasn’t the main trap.
The real trick was the development interface.
Victims were directed to an interface designed to look like Remix and instructed to use it to compile and deploy the contract.
After victims deployed the contract and funded it with their own assets, the attacker was able to drain the funds.
The attacker still appears to hold a significant portion of the stolen funds at these addresses:
0xcf27FAFb41e183C567E23786bB1f3E80a44b8Ef3
0x8d3736f31de511ad19c168973190a2e0c75f776a
Stay smart.
Show more
LATEST: 🚨 TRM Labs says 9 fake YouTube tutorials on building a crypto arbitrage bot with Claude tricked 224 victims into deploying self-draining smart contracts, netting scammers 274.60 ETH over 6 months.
Show more
What's interesting, considering the period covered by the stolen data, is that it likely means the breach had already occurred by April or, at the latest, early May but you chose to keep it silent until recently, around the same time Trezor announced its own data breach.
What's even more concerning is that some of your users were already receiving phishing attempts while some already getting compromised yet you chose not to be transparent, warn users, or create awareness.
Instead, you denied it.
Putting their personal data at risk and still lying to them
Just crazy
Show more


An unknown victim was just drained of $25.6M in assets.
The attacker swapped all the assets, including WBTC, cbBTC, LDO, USDS, and CRV, for DAI and ETH.
Interestingly, the same wallet was drained of $24.23M in September 2023 due to malicious token approvals. The attacker eventually returned approximately 90% of the stolen funds.
Theft address: 0x8fEB0c6eF08B20bA19C04F951d4408bB5A1F95Ae
Stay Smart.
Show more











