Matthew Prince 🌥
@eastdakota
A little bit geek, wonk, and nerd. Repeat entrepreneur, recovering lawyer, and former ski instructor. Co-founder & CEO of Cloudflare (NYSE: NET).
299 Following 355.3K Followers
Some stats on #php2shell#. In the 10 hours before it was publicly announced, across the @Cloudflare network we saw thousands of attempts to exploit it. That jumped to tens of thousands in the 45 minutes post announcement, hundreds of thousands within 2 hours, and millions now.
Show more
Two classes extremely bad cyber vulnerabilities disclosed in the last 24 hours. The first potentially impacts everyone online. The second impacts nearly everyone running a server.
tl;dr: Everyone should upgrade their OS and Browser as soon as possible. If you run a server you should upgrade PHP (or ensure it’s removed if you’re not using it) as soon as possible.
The first class of vulnerabilities is a set of root TLS certificates that were discovered to have a trivial private key. Literally the number 4. These roots were controlled by #eMudhra#. The problem is that with that an attacker could create a certificate and, if they could get in the traffic flow, intercept traffic to any site or service. The solution is to stop trusting certificates issued by these vulnerable roots. Upgrading your browser and OS is the fastest way for most Internet users to do this.
The second class of vulnerabilities doesn’t apply to most consumers directly, but does apply to most anyone running a server. These vulnerabilities have been dubbed #php2shell#. PHP is one of the most widely used web programming languages. It’s estimated 70% of websites run on PHP. These vulnerabilities allow an attacker to send a crafted set of queries to a server running PHP and potentially take over the server. From there they could potentially read, modify, delete, or repurpose anything on the server. The solution is to upgrade PHP to the latest version ASAP. Even if you’re not using PHP for your web development, it’s often included by default. So make sure it is either upgraded or fully removed.
@Cloudflare received advanced warning of both of these classes of vulnerabilities. We’ve ensured that where we act as a proxy we are no longer trusting the vulnerable roots. We are also reviewing certificate transparency (CT) logs for any sign the vulnerability was exploited before its disclosure. We have not found any evidence but CT logs are not perfect and a sophisticated attacker who knew about the weakness could have exploited it without a new certificate being logged.
For the PHP vulnerabilities, we have deployed mitigations available for all customers for free. Because of the complexity of the vulnerabilities and number of ways it can be exploited, we also released new WAF capabilities that are unique in the industry to catch the exploit based on the response. These too are available for every Cloudflare customer for free.
Even if you are taking advantage of Cloudflare’s protection, it is important to upgrade your OS, browsers, and PHP installations as soon as possible. We can provide a strong bandaid, but the best protection is to fix the underlying problem.
If you’re interested in learning more, you can read our blogs:
Vulnerable roots:
PHP vulnerabilities:
Show more

@eric_khun As long as I’m CEO.
Amused that AWS just unilaterally cancelled Cloudflare's Reinvent booth. There are always signs when someone finally realizes they're losing. Guess we'll just attend and throw the most fun side events without paying Amazon! Reply if you want an invite.
Show more

Two medal plates and lots of screws to fix my right humerus, which I shattered in a bike accident in Europe earlier this week. Thanks to the amazing team at @HSpecialSurgery for patching me up better than new. And, yes, I’m insisting @zatlyn call me Iron Man.
Show more

What should we announce tomorrow? #BirthdayWeek#
I’m not supposed to have favorite Birthday Week announcements, just like one shouldn’t have favorite children, but I will say this one is so insanely cool:

Welcome to @Cloudflare's #BirthdayWeek#. As is our tradition, @zatlyn and I penned our annual Founders' Letter to kick the week off:

It’s possible to write bug free code. In ~2 years it’ll be impossible not to.

100 TB of RAM, saved by shrinking a consistent hash ring. The last 90,000 hashes per server were buying 0.7% load balance improvement. Math said stop. We stopped.


!!!ACTION REQUIRED!!!
if you are building something weird and ambitious on cloudflare, I would VERY much like you to come defend your life choices in front of me on stage. it's going to be dope, please sign up TODAY.
Show more
This is what's wrong with San Francisco. ;-)

Jev is now available in Cloudflare Workers AI.


🤯🤯🤯Durable Objects are the best cloud primitive for the agentic era.

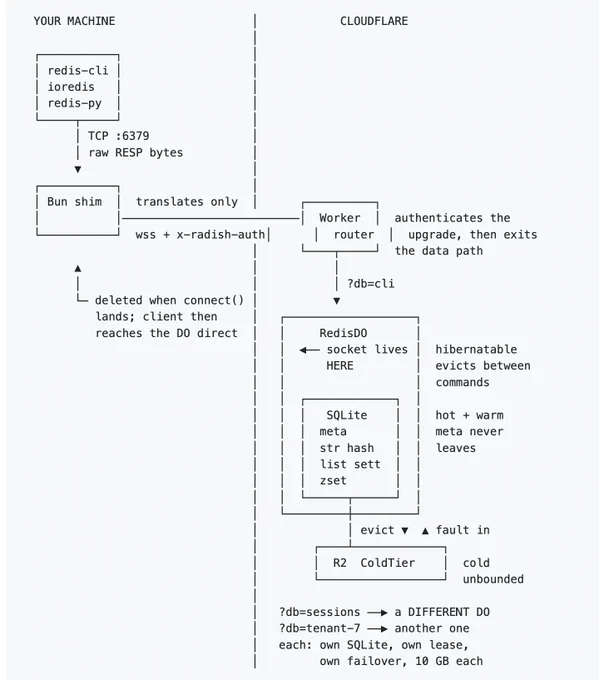
(re) Introducing Radish, it's a redis server completely inside a @Cloudflare durable object.
this weekend I did an experiment to see how good GPT-6 Astra and Fable are now, at systems and database design by revamping Radish (one of my old projects). it was terrible back then lol because i knew nothing about dbs. now that i know a little bit, worth a try!
Not prod-ready (ofc) and it's also a magnitude less QPS than a single node redis server, BUT
It's ACID compliant. It uses durable object sqlite as the hot storage and r2 as the cold storage beyond the 10GB mark. fully serverless!
It's multi-tenant so you can run a redis server PER USER!
Workers and DOs don't have inbound TCP connections yet (it's in their roadmap), but until then, it uses a bun shim to connect to the worker
I verified it using formal methods, also ran it against 200k commands on real redis and made it byte-identical in terms of responses, performance etc.
There's some very interesting things in there too (automatic multi-tenant isolation, unbounded by RAM, fully durable)
There's only two dependencies, @EffectTS_ and @alchemy_run. that's it.
Show more

founders! pitch your startup in a Shark Tank-style competition live on stage at Connect
- win a billboard in SF, $350K in @Cloudflare credits, access to the VIP speakers dinner
- judged by @eastdakota, @zatlyn, @dok2001
- hosted by @threepointone
details + how to apply ↓
Show more
This is a big win in the battle for the future business model of the Internet!
Today, Cloudflare is announcing a new Disallow AI Training setting that lets you easily stay indexed for search while refusing to let that same crawler train on your content.


you can now give any teammate or agent access to just one Worker
we’re starting by bringing granular authz to Workers and are are working on supporting the same for D1, KV, and the rest of dev plat!
here are 4 new roles that you can set to grant the right level of access 👇
Show more

You can now scope access to individual Workers and assign narrower Developer Platform roles, so teammates, CI tokens, and agents get only the access they need to debug, deploy, or monitor safely.
Show more

This is a good coda to @matt_levine’s opening segment today.

Good tennis is fun to watch! #usopen#












