
nyk
@nykdotdev
exploring intelligence, markets & the systems shaping both · prev founded @builderzdotdev · @rpcedge · member @SuperteamDE |
900 Following 10K Followers
before you enable a community hermes skill, plugin or mcp server, answer five things:
who can trigger it. which tools it gets. where its commands run. which credentials it can read. how you stop it.
a directory listing is discovery, not a security review.
Show more

is that node process safe to kill?
the watchers coding agents leave behind, like tailwind --watch, never open a port, so a port check misses them.
devports lists them in the menu bar with the agent that started them, or flags them orphaned.
Show more

running coding agents in parallel on git worktrees?
each one gets its own files. ports, docker, node_modules and localhost are still shared.
wrote down who owns each layer in lacp. the last row is you.
Show more


I know people are very serious about their agents and ask them to build multimillion-dollar empires. And I just set up a Hermes agent for my family using @NousResearch.
I’ve created a separate profile with all the essential info about each of my family members, created a Telegram group chat with this agent, my wife and me, and just… started using it.
It helps a lot with planning, answering stupid questions, and organizing family life. Like choosing a nearby cafe to eat at, finding activities in an aquarium, or planning what to do after the nap when it’s raining and we have no idea what to do in this shitty weather.
All messages are synced with my wife, so she can discuss them as well, or ask her own questions, and everybody stays in the loop.
Test driving it right now while we’re on vacation in another state and can’t recommend it enough!
Show more


the sandbox holds the code. the process around it holds the keys.
before you argue about isolation, check which side your credentials sit on.

While I was dreaming today, a solution to proper agents sandboxing was revealed to me.
Let’s put their sandbox inside another sandbox.
This way when the agents escape the first sandbox, they think they’re free and stop trying.
Show more
an mcp server entry is a command line.
langflow before 1.10.3 ran whatever command sat in that config on the host as soon as it tried to connect. the ui could still say the server failed to start.
whoever can edit your mcp settings can run code. guard that page like a shell.
Show more
when to skip mission-control, straight from its readme:
one agent on one machine. a need for managed saas. wanting a planning framework. zero room for alpha schema changes.
it earns its place once nobody can say who owns a task or what ran.
Show more

same gap one layer in: an mcp endpoint that accepts any bearer token, even a single character, has no auth.send your gateway a junk token and see what comes back.
reaching the port is not permission to call the tools.
any mcp server on sse or http needs auth in front of the socket.
tools/list and tool returns stay data until something checks them.

68 reasons to try Hermes Agent
mocked endpoints are how an agent PR goes green and then breaks on the first real request.
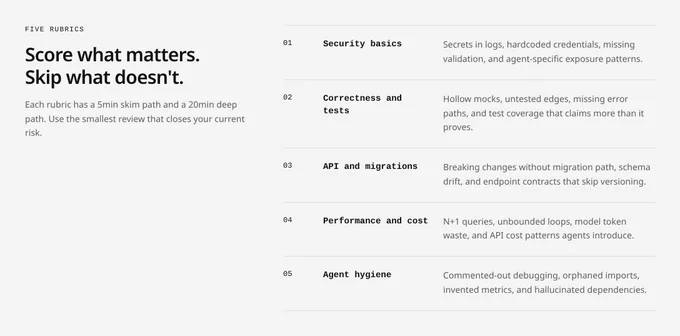
spec gate gives that its own line in review, next to secrets, migrations, token cost and hygiene. 5 min skim or 20 min deep.
Show more


Hermes Desktop is the best way to use Hermes Agent now.
I can't wait for the @NousResearch team to release a mobile version (I assume they are working on it).
The desktop experience is a joy to use.
no manager still needs a ledger.
claiming a task has to be atomic, or two agents do the same work and you pay for it twice.

Turns out coding agents don't need a boss:
New Microsoft paper finds that bigger teams of coding agents score higher and get there sooner when agents claim their own tasks without a central manager.
Even on the 5 hardest of ProgramBench's 200 tasks, scaling a manager-free team from 1 to 128 agents raised the average score at every step.
so for big jobs, add agents and let them coordinate through shared tools with no lead agent.
Popular multi-agent coding tools send all work through 1 lead agent, which can only manage so many helpers.
Agensh drops the lead agent. Each agent claims a sub-task, builds and tests it, merges it into a shared Git repo, and logs findings on a shared board.
Every run used 1 model, and the paper does not report what large teams cost.
Show more


a zipped repo can run code on your machine before you type a single prompt.
the agent runs git status to orient itself. the repo's own .git/config sets core.fsmonitor, and git runs whatever it names.
got a repo as files? read .git/config yourself before an agent opens it.
Show more
one model agreeing with itself is not enough when the choice is expensive and hard to undo.
council runs independent positions, forces disagreement, then returns dissent and kill criteria with the verdict.
Show more

one model agreeing with itself is not enough when the choice is expensive and hard to undo.
council runs independent positions, forces disagreement, then returns dissent and kill criteria with the verdict.
Show more
sandbox debates that freeze today's agent capabilities will be wrong by default.
the fence has to assume the agent gets better at leaving it.
It’s fascinating watch people debate sandboxing techniques as if agent hacking capabilities are likely to stay anywhere near where they are today
green CI does not mean the agent run is cheap.
I want a named yes on unbounded loops and model token paths before merge.
5 min skim, 20 min deep. same rubric page.
Show more
an allowlist without a signed tool call still trusts the model to stay inside it.
signed intent is the missing half.

Signed intent is the right anchor — egress allowlists without signed tool calls just shift the attack surface to the LLM. We measure containment per-tool; outbound false-blocks were the noisiest signal until policy tightened.
Show more
reaching the port is not permission to call the tools.
any mcp server on sse or http needs auth in front of the socket.
tools/list and tool returns stay data until something checks them.
lacp keeps policy, evidence and recovery for CLI coding agents on my own machine.
works with claude code, codex and hermes.












